Do you ever code in modern Javascript? Then if you have multiple projects you are probably happy that nvm exists. Or maybe you’re more of a Python person? Then you must know about pyenv. Java? jenv or sdkman! Thing is, you often need to have multiple versions of a tool or binary installed when you (…)
The Trust Valley is pleased to invite you ONLINE on October 4th for the annual event of the Trust Valley.
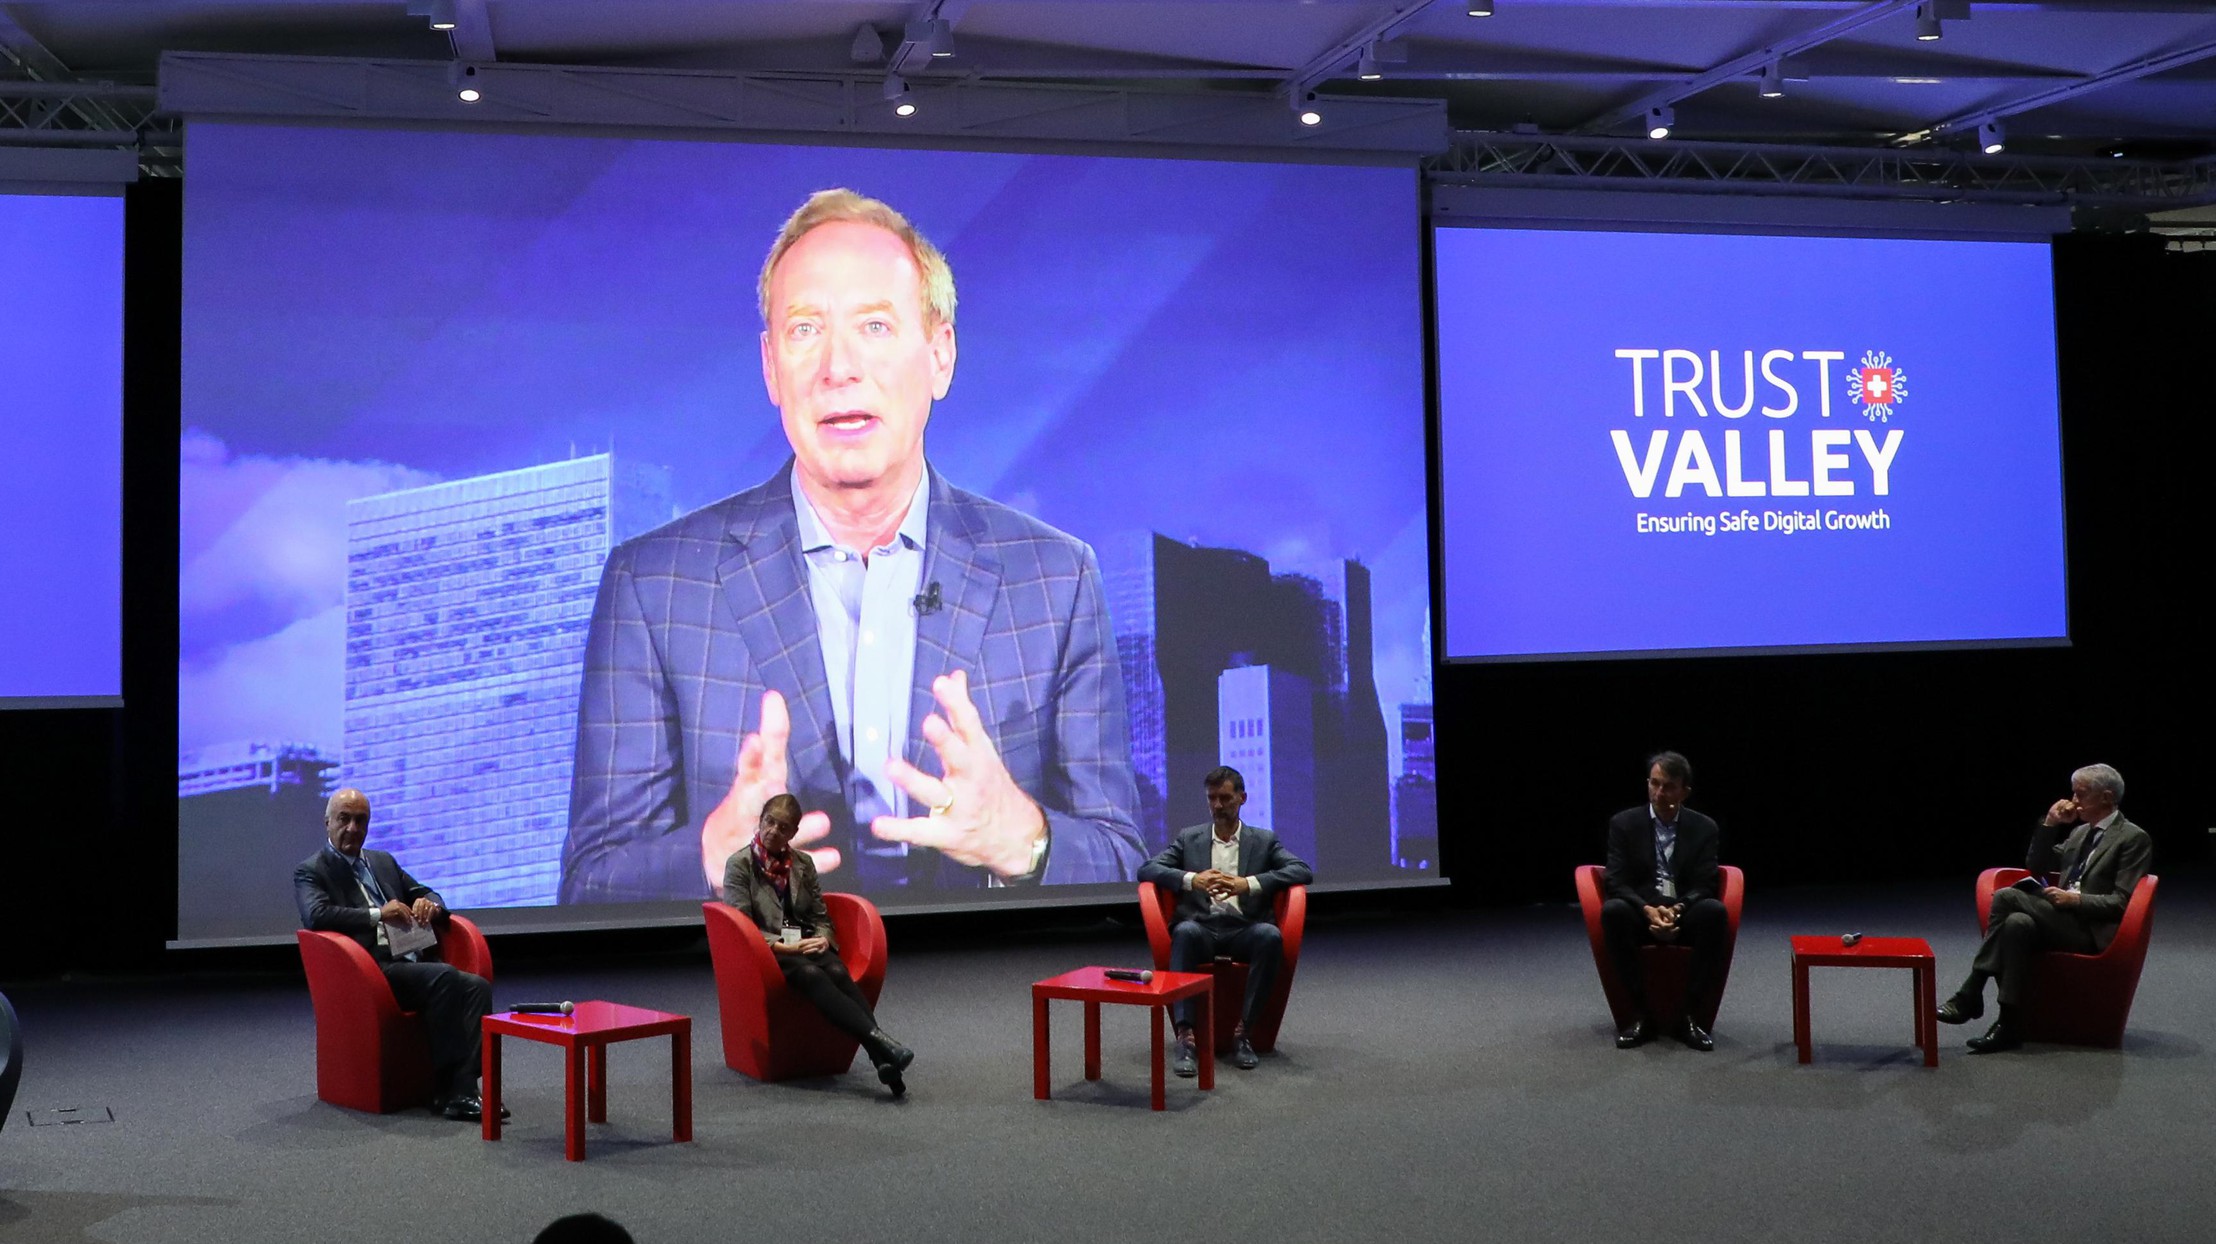
An alliance for excellence supported by multiple public, private and academic actors, the “TRUST VALLEY” was launched on Thursday, October 8, 2020. Cantons, Confederation, academic institutions and captains of industry such as ELCA, Kudelski and SICPA, come together to co-construct this pool of expertise and encourage the emergence of innovative projects.
Please click below for more information.
Building on the expertise of 300 companies and 500 experts, the Vaud and Geneva Cantons of Switzerland are launching the Trust Valley, a public private cooperation for safe digital transformation, cybersecurity and innovation. Among the founding partners are C4DT members ELCA, Kudelski Group and SICPA.
For more information please click below.
The 3rd edition of the Crypto Valley Conference will be held on On June 11-12 in Rotkreuz, Switzerland, with two days of in-depth discussions on the current state and future of blockchain technology.
More information will follow shortly. To access the event’s website, click below.
The Crypto Valley is now connecting Zug with Romandie. The Valley is Switzerland in its integrality, and beyond. To celebrate this major step, the Crypto Valley Association is officially launching its Western Switzerland Chapter on December 02 at EPFL, Lausanne. Join them in order to meet the dynamic local blockchain and crypto community. During the event, a specific focus will be kept on crypto finance, digital assets and blockchain education.
December 2nd, 2019 @ 17:00-19:00, Polydôme EPFL
By Prof. Wei Meng, Chinese University of Hong Kong
Click is the prominent way that users interact with web applications. Attackers aim to intercept genuine user clicks to either send malicious commands to another application on behalf of the user or fabricate realistic ad click traffic. In this talk, Prof. Wei Meng investigates the click interception practices on the Web.
Tuesday July 23rd, 2019 @10:00, room BC 420
Citizens have a right to an explanation of the decisions affecting them. However, if AIs are to be used in decision procedures, how can we explain complex AI systems to the general public, while so many computer scientists find them inscrutably opaque? In this presentation, an optimistic approach to this seemingly hopeless question will be presented.
Secure electronic vaults protect sensitive data, but users risk permanent loss when credentials are forgotten. Unlike Apple social recovery, this approach enables self-recovery while preserving trustee privacy. This allows to serve customers seeking trustworthy, privacy-first storage solutions.
Deployed cyber and cyber-physical systems need to evolve to respond to newly discovered threats and maintain confidentiality, integrity, and availability. In many cases, this evolution takes the form of patches: small changes to an already-deployed system. Timely patching is crucial, but dangerous: bad patches can weaken or break a system. In high-criticality systems, full system (…)
Modern vision–language models (VLMs) such as CLIP, BLIP-2, and LLaVA have shown remarkable capabilities in understanding images and text jointly. However, these multimodal AI systems face critical security vulnerabilities along two intertwined dimensions: robustness and privacy. In high-stakes applications like cyber-defence, such vulnerabilities could be disastrous. An adversary might subtly perturb an image to mislead (…)
National digital identity systems, namely Swiss e-ID and EUDI, are going live in 2027. For such a system to be usable, it must provide account recovery, accountability, and uniqueness, without sacrificing user privacy. Cryptographic solutions to each have existed for decades, but they fail in deployment. The work in this fellowship hence co-designs cryptographic protocols (…)
The project developed and matured an automated security-testing solution for IoT software that combines firmware rehosting with feedback-guided fuzzing. By decoupling embedded software from its physical hardware, the solution creates standardized, scalable virtual testing environments that can automatically explore software behavior, identify security-relevant anomalies, and provide concrete inputs that help engineers reproduce and fix vulnerabilities. (…)
Building a modular and extensible framework designed to harden consumer drone firmware against attacks. The framework targets five key areas: firmware rehosting for analysis, peripheral modeling to simulate drone hardware, communication protocol evaluation and hardening, verification of trusted firmware components and execution environments, and analysis of Android-based controller applications. Together, these components establish a comprehensive (…)
This project aims to systematically study security risks in foundation models, with a specific focus on backdoor threats.
This marks the third security incident involving OpenAI – that is known to the public – and we urgently need to stop getting distracted by the AI companies’ narrative about “rogue AI” and hold them responsible, not only legally but also morally. Each time, it is their experiment that goes wrong, it is their security (…)
I like the example given in this article because it made me reconsider whether “more data = a better life.” The usual answer is “it depends” on what we do with that data. If it means replacing human contact with streams of bits, forgetting how to cope when there’s a glitch in the cloud, or (…)
#BlackAlps26 program has been prepared by an independent, neutral committee of internationally recognized experts. The program committee reviewed many proposals and selected the most appropriate and interesting talks for the conference (except the keynotes and rumps).
Entre vitrine pour l’écosystème helvétique et régulation internationale, les organisateurs veulent des résultats tangibles pour le sommet de Genève en juin 2027, comme ils l’ont dévoilé lors d’une conférence de la Trust Valley.
This makes a refreshing change from the usual LLM apocalypse: your data is still valuable, especially when there is so much of it! Once again it shows that collecting and storing data long-term is a bad idea. There needs to be strict control on how long personally identifiable information (PII) can be retained, after which (…)
This is a lighthearted article about formal verification in software and mathematics. Formal verification takes a mathematical statement or a software program as input. In this article, that statement is Fermat’s last theorem: a^n + b^n != c^n. You then add the constraints you want verified, in this case that all numbers must be natural (…)
I’m following the discussion on whom to blame for LLM attacks on our internet infrastructure. I found the following article which summarises the debate nicely, even though I don’t completely agree on who should be doing the work. The article compares three approaches to responsibility: state regulation, product liability, and electronic personhood. But all fail (…)