
C4DT Track “Your Data, Your AI — Keeping the Keys”
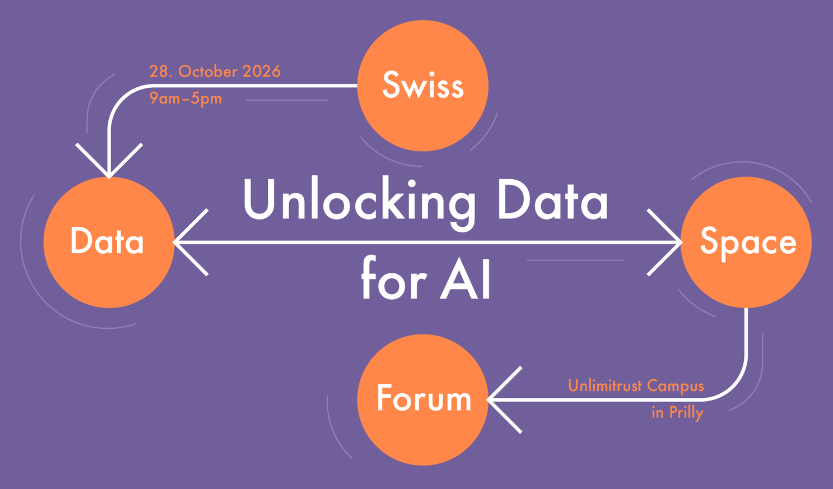
October 28th, 2026, 13h30-14h45, Unlimitrust Campus, 42 Route des Flumeaux, 1008 Prilly
This track is part of the Swiss Data Space Forum 2026, Unlocking Data for AI, organised by digitalswitzerland, under the forum theme “Control Your Data”.
In brief: Unlocking data for AI should not mean handing it over. This 75-minute track shows, through working examples from EPFL’s Research Computing Platform and the EPFL spin-off Anyway Systems, that sovereign AI is operational today. It then asks what else a serious deployment needs: enterprise cloud strategy, cryptographic access control, and governance that makes technical control trustworthy. Organised by the Center for Digital Trust (C4DT) at EPFL, it is aimed at decision-makers and practitioners who deploy or oversee AI.
Introduction
The forum’s premise is that unlocking data will unlock AI. But unlocking data means little if organisations surrender control of it to cloud platforms subject to foreign jurisdiction or to opaque inference pipelines.
“Keeping the keys” has two meanings. It means retaining control of your data in an age when sharing it feels inevitable. It also means cryptographic key management, the mechanism that makes that control real even when data lives outside your own infrastructure. Unlock the data, by all means. Just make sure you keep the keys.
This track argues that organisations can deploy powerful AI and retain control of their data, but only if sovereignty is built into the infrastructure around it from the start. To be trustworthy, however, AI deployments also need governance from the start.
Two EPFL initiatives show this is already being done. EPFL’s Research Computing Platform runs open-source large language models entirely on campus. Anyway Systems, an EPFL spin-off, turns ordinary on-premise hardware into a distributed inference cluster that can run frontier models without any cloud dependency. A panel of practitioners and policy experts from ELCA, DuoKey and C4DT then looks at what Swiss enterprises and institutions do with that capability, and what layers of governance and cryptography make it trustworthy end to end.
This track is organised by the Center for Digital Trust (C4DT), EPFL.
Objectives
- To show that sovereign AI is operational today, not a future ambition.
- To demonstrate that unlocking data for AI and controlling that data are not in tension, but that control must be designed in from the start, and that trust requires governance from the start too.
- To give attendees a practical map of what data control requires across the full stack: from model hosting and cloud strategy to cryptographic access, operational governance and public trust.
For questions about the track, please contact david.viollier@epfl.ch
Agenda
13h30
Welcome and Framing
by David Viollier, C4DT, EPFL
The forum wants to unlock data for AI. This track asks what it means to do so without giving away the keys. Holding the keys is the foundation. Deciding who may use them, for what, and under whose oversight is what turns control into trust.
Part 1: Sovereign AI Is Operational Today
Two working examples, from a university and from a spin-off, of running powerful open-source models entirely on your own infrastructure.
13h32
Talk – Sovereign AI for the EPFL Community
by Matéo Muller, System Specialist, Research Computing Platform (RCP), EPFL
Abstract: For over a year, the EPFL community has been using powerful open-source language models running on campus infrastructure, in production and in daily use. This talk shares what it took to get there and what a year of production has taught: the technical choices, the governance decisions, and what it means in practice for researchers and staff who want AI assistance without compromising the sensitivity of their work.
13h50
Talk – Sovereign AI for All: Running Large Open-Source LLMs Locally
by Geovani Rizk, CEO, Anyway Systems (EPFL spin-off
Abstract: Anyway Systems was built on a simple premise: every organisation should be able to run state-of-the-art AI on its own infrastructure, without sending a single byte to a third party. This talk explains how the system combines on-premise machines into an optimised AI cluster, so that any organisation, public or private and not just the cloud giants, can run fully sovereign AI of its own.
Part 2: Control Needs Keys, Trust Needs Governance
The two talks establish that sovereign AI infrastructure is buildable. The panel broadens the conversation to what Swiss enterprises and institutions actually do with that capability, and what layers of governance and cryptography are needed to make it trustworthy end to end.
14h08
Panel Discussion – Keeping the Keys: Data Control from Deployment to Governance
Moderated by: David Viollier, C4DT, EPFL
Panelists
- Maxime Claux, VP Cloud, ELCA/EveryWare Group
- Grégory Ruch, Head of Security, DuoKey
- Paola Daniore, Digital Trust Policy Fellow, C4DT, EPFL
14h43
Wrap-up
by David Viollier, C4DT, EPFL